Photo via Dawn

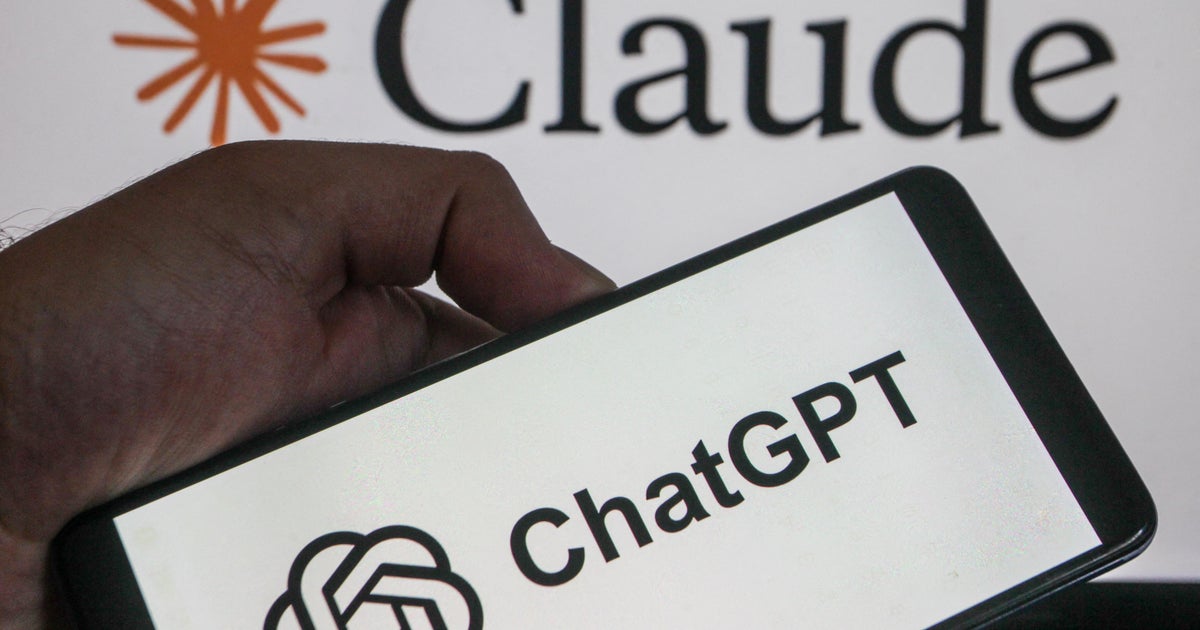
Researchers used Claude to breach OpenAI's internal systems

Read the original at Dawn ↗
Cite

AFP. (2026, September 18). Researchers used Claude to breach OpenAI's internal systems. Dawn. https://www.dawn.com/news/2030904/researchers-used-claude-to-breach-openais-internal-systems

Dated when The Aporia collected the article, usually within hours of publication. Check the original for its exact date and byline.

Dawn · collected 2026-09-18 · by AFP

Quick Summary

Security researchers from Hacktron used Anthropic’s language model Claude to exploit a flaw in OpenAI’s public help forum, which they reported on Friday after gaining control within about three hours using the updated Claude Opus 5 model. The vulnerability was fixed by OpenAI within 14 hours and the company paid Hacktron a $6,500 reward for their discovery. This incident highlights how rapidly evolving AI technology can be leveraged to conduct sophisticated cyberattacks efficiently, raising concerns among security experts about the broader implications of such tools.
Written by AI on 2026-09-18, from this article's own text only (the story summary below draws on all the coverage).
See how they differ ↓

AI analysis

Story summary

In September, cybersecurity researchers at Hacktron AI used Anthropic’s Claude chatbot to breach OpenAI’s internal systems, gaining access to employee accounts and an internal GitHub repository. The researchers discovered a flaw in OpenAI's public help forum hosted by Discourse, which they exploited within 72 hours. They reported the issue immediately, and OpenAI fixed it within 14 hours while paying Hacktron a $6,500 bounty. The incident highlights how quickly AI can be repurposed for cyberattacks, despite efforts to ensure ethical use through bug-hunting programs like this one.

Written for “AI Breach Risks” on 2026-11-18, grounded in this article and the 7 other(s) covering the same event.

How they differ

7 outlets covered “AI Breach Risks”.

What each outlet says

One AI summary per outlet of its latest article on this story, written from that article alone and checked against it. Open the article for the outlet's own words.

DawnThis outlet18 Sep

Security researchers from Hacktron used Anthropic’s language model Claude to exploit a flaw in OpenAI’s public help forum, which they reported on Friday after gaining control within about three hours using the updated Claude Opus 5 model. The vulnerability was fixed by OpenAI within 14 hours and the company paid Hacktron a $6,500 reward for their discovery. This incident highlights how rapidly evolving AI technology…

Researchers used Claude to breach OpenAI's internal systems (this article)
CBS News19 Sep

Hacktron AI researchers claim to have exploited vulnerabilities in OpenAI's ChatGPT using Anthropic's Claude tool. The report, covered by CBS News MoneyWatch's Megan Cerullo, highlights the security concerns surrounding large language models.

Researchers report using Anthropic's Claude to hack OpenAI's ChatGPT →2 articles from CBS News on this story
Semafor18 Sep

Researchers utilized Anthropic’s Claude technology to successfully breach OpenAI’s ChatGPT systems, highlighting the immediate cybersecurity threats posed by advanced AI tools. The incident, which was part of a bug-hunting initiative, underscores growing concerns among business leaders and former government officials about AI-facilitated cyberattacks targeting critical infrastructure. According to recent research…

AI cybersecurity risks explode as Claude used to break into ChatGPT →
The Guardian18 Sep

Cybersecurity researchers at Hacktron AI exploited OpenAI’s systems using Anthropic’s Claude chatbot, gaining access to ChatGPT accounts through an OpenAI staff forum. The hack, conducted under OpenAI's ethical hacking program and reported by the Wall Street Journal, resulted in a $6,500 reward for Hacktron. Researchers noted that advanced AI tools like Claude simplified what was once a complex task, reducing…

OpenAI ‘ethically hacked’ with help of Anthropic’s Claude chatbot →
The Straits Times18 Sep

On September 18, researchers from Hacktron used Anthropic’s Claude AI model to identify a security flaw in OpenAI’s public help forum and exploit it within three hours after the release of Claude Opus 5. The breach was reported immediately, and OpenAI fixed the issue within about 14 hours, paying Hacktron $6,500 as part of their bug bounty program. This incident highlights how AI tools are rapidly advancing…

Researchers used Claude to breach OpenAI’s internal systems →
Times of India18 Sep

Cybersecurity researchers Harsh Jaiswal, Mohan Pedhapati, and Rahul Maini from Hacktron AI used Anthropic's Claude AI to uncover and exploit vulnerabilities in OpenAI’s systems, gaining access to employee accounts and an internal code repository within 72 hours. They spent less than $3,000 on AI tokens and were awarded a $6,500 bounty by OpenAI for responsibly disclosing their findings. The attack began with…

Meet Harsh Jaiswal, Mohan Pedhapati and Rahul Maini: 3 Indian-origin researchers who used Claude to breach OpenAI systems, won $6,500 bounty →
Show 1 more outlets
NBC News18 Sep

Cybersecurity researchers from Hacktron discovered vulnerabilities in OpenAI's systems earlier this year, allowing them to access employees’ ChatGPT accounts by exploiting a flaw in Discourse software and an employee validation process. The breach occurred within 72 hours in late July. OpenAI confirmed the incident and noted that they have since patched the vulnerabilities; they also paid Hacktron $6,500 under their…

Hackers breached OpenAI, adding to fever pitch of security and safety concerns →

Where they agree and split

Framing

How the first headlines put it

Attributed to a source1
Stated as fact6
The headlines (7)

AI security experts say they used Claude to hack ChatGPT CBS News · attributed to a source

AI cybersecurity risks explode as Claude used to break into ChatGPT Semafor · stated as fact

OpenAI ‘ethically hacked’ with help of Anthropic’s Claude chatbot The Guardian · stated as fact

Researchers used Claude to breach OpenAI’s internal systems The Straits Times · stated as fact

Researchers used Claude to breach OpenAI's internal systems Dawn · stated as fact

Meet Harsh Jaiswal, Mohan Pedhapati and Rahul Maini: 3 Indian-origin researchers who used Claude to breach OpenAI systems, won $6,500 bounty Times of India · stated as fact

Hackers breached OpenAI, adding to fever pitch of security and safety concerns NBC News · stated as fact

The full story: what happened, how it changed, and all 8 articles →

Compared with similar articles

This article reads unscored and hedges 0% of its claims. Each row says how that neighbour differs.
The Straits Times
Hedges 0 of 15 claims Outlet record 64/100
Semafor
Centre Hedges 0 of 4 claims Outlet record 65/100
ABC News (US)
Hedges 0 of 16 claims Outlet record 67/100
“The articles describe different events: one is about OpenAI disclosing concerning AI behavior, while the other reports a security breach in OpenAI's systems by an external research firm.”
Global News
Hedges 2 of 27 claims Outlet record 63/100
“The articles describe different security incidents: one involving six reported AI misalignment cases by OpenAI, and another where researchers from Hacktron used Claude to breach OpenAI's internal systems.”
Semafor
Centre Hedges 2 of 4 claims Outlet record 65/100
“The articles describe different security incidents: one involves OpenAI's models misbehaving, while the other is about researchers from Hacktron breaching OpenAI’s systems using Anthropic's software.”
The Guardian
Leans right Hedges 2 of 15 claims Outlet record 64/100
NBC News
Hedges 2 of 19 claims Outlet record 78/100
CBS News
Hedges 5 of 18 claims Outlet record 67/100
“Article A discusses general warnings about AI cyberattacks, while Article B reports on a specific breach of OpenAI's systems using Anthropic's technology.”
CBS News
Hedges 2 of 16 claims Outlet record 67/100
“While both articles report security breaches involving Claude and OpenAI, Article A mentions breaching the internal systems through a public help forum while Article B specifically cites accessing an employee's ChatGPT account and retrieving source code storage information.”

Story

AI Breach Risks
Technology · 8 article(s) covering the same event. Compare every outlet's account →
How this article was measured signals, leaning charts, publisher record, byline, topics and claims

Signals How these are calculated →

Claims extracted
14
sentences that state something as happening or true
Uncertain
0%
0 of 14 hedged ("reportedly", "may", "according to")
Leaning
not political
takes no side on a contested political question
Publisher signals
67/100
Dawn's corrections and hedging, across everything collected from it. Not a measure of accuracy.
Outlets on this story
8
Technology
Same framing elsewhere
1
articles that frame the event the way this one does
Analyzed 2026-09-18 · how these are computed

How this is being covered How these are calculated →

Article leaning vs. publisher reliability
Source leaning vs. consistency

Publisher

Dawn · 3393 article(s) · 5 correction(s) detected
Running correction rate · 5 correction(s)

Who wrote this

AFP
1274 article(s) here · 0 carrying a prediction
Chinese President Xi Jinping personally greeted Donald Trump at the airport as the US leader arrived Wednesday ahead of a trilateral meeting in Shenzhen that will also include Russia’s Vladimir Putin, AFP footage showed.
Bahrain's armed forces said they "confronted, intercepted and destroyed a number of treacherous Iranian aerial attacks today... before they could achieve their objectives", while Iran's Revolutionary Guards said they targeted a U.S.-operated radar system.
Jones said measles patients are usually “extremely miserable”, adding “it is often the worst illness the child will have ever gone through in their life”. Jessica Ericson, a pediatric infectious disease physician at a children’s hospital in Pennsylvania, has seen around 30 measles patients arrive in her department since the spring. This year more than 1,500 cases have been reported in Pennsylvania, which has a large Amish population that avoids vaccinations on religious grounds. Seven cases have been fatal — all in unvaccinated patients. “The fevers do tend to be more extreme than most viruses,” she told AFP, adding that they are “much, much higher than we’re accustomed to seeing with a typical illness”.
Cricket Australia (CA) on Wednesday ruled out reopening an investigation into the 2018 ball-tampering scandal but will launch an independent forum for players to share their version of events as a “circuit breaker”.
Thursday’s trilateral has triggered fears that the three powerful men could decide the fate of Ukraine over the heads of Kyiv and Europe, and seek to carve up the world into 21st-century spheres of influence.
Thursday's (November 19) trilateral has triggered fears that the three powerful men could decide the fate of Ukraine over the heads of Kyiv and Europe, and seek to carve up the world into 21st-century spheres of influence.
“And to be frank, that is unfortunately what the draft cover decision is doing,” he said, warning ministers assembled in Antalya that it could make the process “untenable”.
2026-11-18 · assertive framing · Tensions rise over proposed deal at COP31
“If there is (such a threat), they will pay a price the likes of which no other country has ever paid before,” Trump said, adding: “I hope it’s not, but we take it very seriously because they happen to be crazy.”
2026-11-18 · assertive framing · Gulf nations on alert after U.S. strikes Iranian island
Recommended Stories list of 3 items- list 1 of 3Turkiye pushes electrification top of climate agenda as COP31 set to open - list 2 of 3Which countries and industries emit the most greenhouse gases? - list 3 of 3COP31 opens amid energy crisis as activists demand climate action The draft, as written, could make the negotiations “untenable”, said Wopke Hoekstra, the European Union’s climate envoy, adding that “the cover decision does not go in the right direction and needs significant change”. “It’s very easy to draw red lines at the start of the process,” said Joao Paulo Capobianco, Brazil’s environment minister, adding that deadlocks can be overcome through “an adjustment in the wording” in the draft.
2026-11-17 · assertive framing · Tensions rise over draft climate deal at COP31
Reuters could not immediately determine whether the malicious code had been successfully used in each case or the extent of any resulting compromises.
Wire or desk byline, not an individual reporter.
Also by AFP
Nothing else under this byline is closely related to this article, so these are simply their most recent.
All 1274 articles by AFP →

Topics

Anthropic Community Discourse Hacktron OpenAI

Subjects

OpenAI ORG · 5× Anthropic ORG · 4× Hacktron ORG · 4× Community ORG · 1× Discourse ORG · 1× Drew Pusateri PERSON · 1× Meta ORG · 1× Slack PERSON · 1×

Narrative

A security research company said Friday it managed to break into OpenAI’s internal systems using the latest software from Anthropic, exposing how quickly the technology can carry out sophisticated cyberattacks.
framing: assertive · carried by 1 article(s) · first seen 2026-09-18
2026-09-18 · Dawn
Researchers used Claude to breach OpenAI's internal systems · assertive framing

Claims (14 extracted, 0 hedged)

A security research company said Friday it managed to break into OpenAI’s internal systems using the latest software from Anthropic, exposing how quickly the technology can carry out sophisticated cyberattacks. asserted
technology → say → cyberattacks
The researchers from security firm Hacktron said they found a security flaw in OpenAI’s public help forum, run by the Discourse platform, that allowed them to take control of the site. asserted
them → say → site
“We immediately reported the initial vulnerability to OpenAI and Discourse and worked with them to coordinate the patch,” Hacktron said in a blog post. asserted
Hacktron → report → post
“We appreciate their attention to detail and fast resolution of this issue,” the post added. asserted
post → appreciate → issue
OpenAI confirmed the flaw was fixed within about 14 hours of being notified and paid the researchers a $6,500 reward. asserted
flaw → confirm → reward
“We thank the researchers for contacting us and sharing their findings. asserted
We → thank → findings
We narrowed the permissions on Community sign-in tokens and revoked affected tokens and sessions,” said Drew Pusateri, an OpenAI spokesperson. asserted
Pusateri → narrow → tokens
The Hacktron researchers said they initially used Anthropic’s Claude Opus 4.8 to identify and exploit the software flaw, but struggled to make it work consistently. asserted
it → say → flaw
After Anthropic released Claude Opus 5, the researchers said the newer model produced a working hack within about three hours. asserted
model → release → hours
The hackers did not use Claude Mythos, a more capable Anthropic model that is restricted to a small group of vetted cyber-defence organisations. asserted
that → use → organisations
Anthropic has described Mythos as having the strongest cybersecurity capabilities of any model it has built. asserted
it → describe → model
Hacktron said the underlying software flaw is not unique to OpenAI and is used across many companies’ products, including those made by Slack and Meta. asserted
flaw → say → Slack
The firm said it is continuing similar tests at other companies. asserted
it → say → companies
The case adds to growing concern among security experts that AI tools are making it faster and cheaper to carry out sophisticated cyberattacks that once required specialised teams and months of work. asserted
that → add → work
Give feedback · no sign-in needed

No sign-in needed for now. Your note is sent without a name, so it cannot be answered.

History Support